A cloud access security broker (CASB) is a security tool that sits between your users and the cloud applications they use, giving you visibility into which apps are in use and control over who can access them and what data goes in and out. It brings the kind of policy control companies once had over on-premises systems to SaaS apps like Microsoft 365, Google Workspace, Salesforce and file-sharing services. Today, CASB is most often bought as part of a larger SSE or SASE platform rather than as a standalone product.
At a glance
- A CASB discovers cloud app use, including apps IT never approved (shadow IT), and rates their risk.
- It enforces policies on access, sharing, uploads and downloads in cloud apps.
- It applies data protection controls, such as finding and restricting sensitive data stored or shared in SaaS.
- It works through API connections to approved apps, inline proxies in the traffic path, or both.
- It is now commonly one component of a security service edge (SSE) or SASE platform.
What problem it solves
As companies moved email, files and business applications to the cloud, much of their sensitive data left the network that firewalls and on-premises tools could see. Employees sign up for apps on their own, share files with personal accounts, and access company data from unmanaged devices. IT often has no inventory of what’s in use and no way to enforce rules once data is in a third-party service.
A CASB restores that visibility and control. It can show that hundreds of cloud apps are in use when IT expected dozens, flag a folder of customer records shared with “anyone with the link”, stop an upload of sensitive files to a personal storage account, or require extra verification when someone signs in from an unfamiliar device. That matters for data protection, compliance audits and limiting what an attacker can reach with a stolen account.
How it works
Discovery. By analyzing firewall or proxy logs, or traffic passing through its own proxy, a CASB builds an inventory of cloud apps in use and scores their risk based on factors like security practices and data handling.
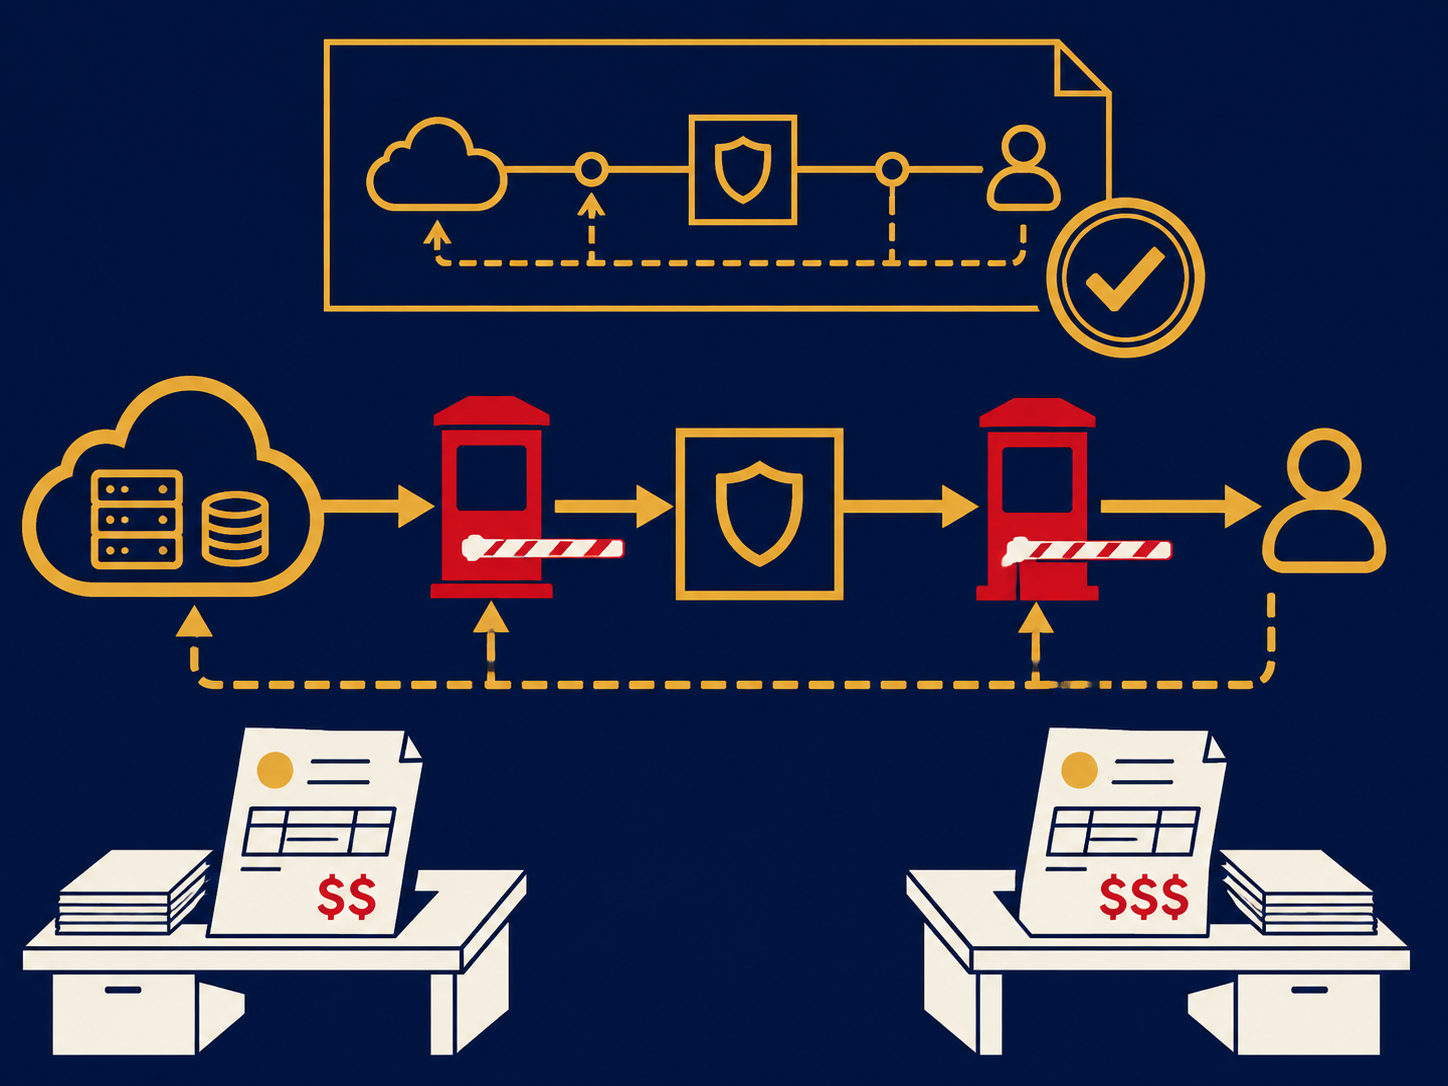
API mode. For sanctioned apps, the CASB connects to the app’s API with administrator approval. It can scan stored files for sensitive data, review sharing settings, check configurations, and detect unusual account activity. Because it isn’t in the traffic path, it can’t block an action as it happens but can fix things after the fact, such as removing public sharing.
Inline (proxy) mode. The CASB sits in the traffic path, either through an agent or forward proxy on the user’s device or network, or a reverse proxy tied to the app’s sign-in. It can then enforce policies in real time: block uploads of sensitive data, allow read-only access from unmanaged devices, or block risky apps altogether.
Policy and data protection. Policies combine user, device, location, app and data type. Many CASBs include data loss prevention (DLP) to identify sensitive content such as payment card or health data.
When it matters for buyers
- When SaaS use has outgrown IT’s view. If you can’t list the cloud apps your company uses, discovery alone is valuable.
- When compliance covers data in SaaS. Regulations and audits increasingly ask how you protect sensitive data in cloud apps, not just on your network.
- When evaluating SSE or SASE. CASB capability, and especially the depth of API integrations with the apps you actually use, varies widely between platforms.
- When employees use unmanaged devices. Inline controls can allow access while limiting downloads.
Questions to ask vendors
- Which SaaS apps do you support through API integration, and what can you see and fix in each?
- Do you support inline (proxy) enforcement, and does it require an agent on devices?
- How do you handle encrypted traffic, and which apps or sites are excluded from inspection?
- Is data loss prevention included, and does it share policies with our email and endpoint DLP?
- Is CASB sold standalone or only as part of an SSE or SASE bundle, and how is it licensed?
- How is shadow IT discovery delivered, and how current is your app risk catalog?
How it differs from a secure web gateway and SSE
A secure web gateway (SWG) controls general web browsing, filtering sites and blocking malicious downloads. A CASB focuses on cloud applications and the data inside them, including stored files that never pass through a gateway. Security service edge (SSE) combines CASB, SWG and zero trust network access (ZTNA) in one cloud-delivered platform, and SASE adds networking such as SD-WAN. See our cloud access security broker overview and our post on 3 areas to consider in a work-from-anywhere security policy.
Problems this helps with
- Not knowing which cloud apps employees are using
- Sensitive files shared publicly from Microsoft 365, Google Drive or Box
- Staff uploading company data to personal or unapproved apps
- Auditors asking how we control data in SaaS