Data loss prevention (DLP) is a category of security tools, and the policies that drive them, that identify sensitive information, such as customer records, payment card numbers, health data or intellectual property, and control how it is shared and moved. When someone tries to email, upload, copy or print data in a way that breaks policy, DLP can log it, warn the user, block the action or encrypt the data. It covers data in motion across networks, data at rest in storage and data in use on devices, though which of these a given product covers varies.
At a glance
- DLP finds sensitive data and enforces rules on where it can go, through endpoints, email, web traffic and cloud apps.
- It recognizes data by patterns, keywords, fingerprints of known documents, classification labels and, in many products, machine-learning classifiers.
- Actions range from monitoring and user warnings to blocking, quarantining or encrypting.
- It reduces the risk of accidental and deliberate leaks through the channels it covers; it doesn’t stop every leak.
- It is now often delivered inside broader platforms: SSE/SASE, CASB, email security and endpoint or productivity suites.
What problem it solves
Sensitive data moves constantly: attachments to partners, files synced to personal cloud storage, spreadsheets copied to USB drives, records pasted into chat or AI tools. Most of it is legitimate, some is careless, and occasionally it is deliberate theft by an insider. Without controls, an organization often finds out only after a data breach or a customer complaint.
DLP gives security and compliance teams visibility into how sensitive data is handled and a way to enforce rules on it. It helps prevent the most common accidental leaks, raises the cost of deliberate ones, and produces evidence that data protection obligations, such as those for personally identifiable information and protected health information, are being taken seriously.
How it works
Discovery and classification. DLP tools scan file shares, cloud storage, SaaS apps and endpoints to find where sensitive data sits. Many use or apply data classification labels so that policies can follow the data.
Content inspection. To recognize sensitive content, DLP uses pattern matching (for example, card or ID number formats), keyword dictionaries, exact matching against known records, fingerprints of specific documents and, in many products, machine-learning classifiers. Context such as the user, destination and device is also considered.
Policy enforcement. Rules say what is allowed: for example, no payment card numbers to external email, no uploads of labeled files to personal cloud storage, no copying of source code to USB drives. When a rule is matched, the tool can log, warn and let the user justify, block, quarantine or encrypt.
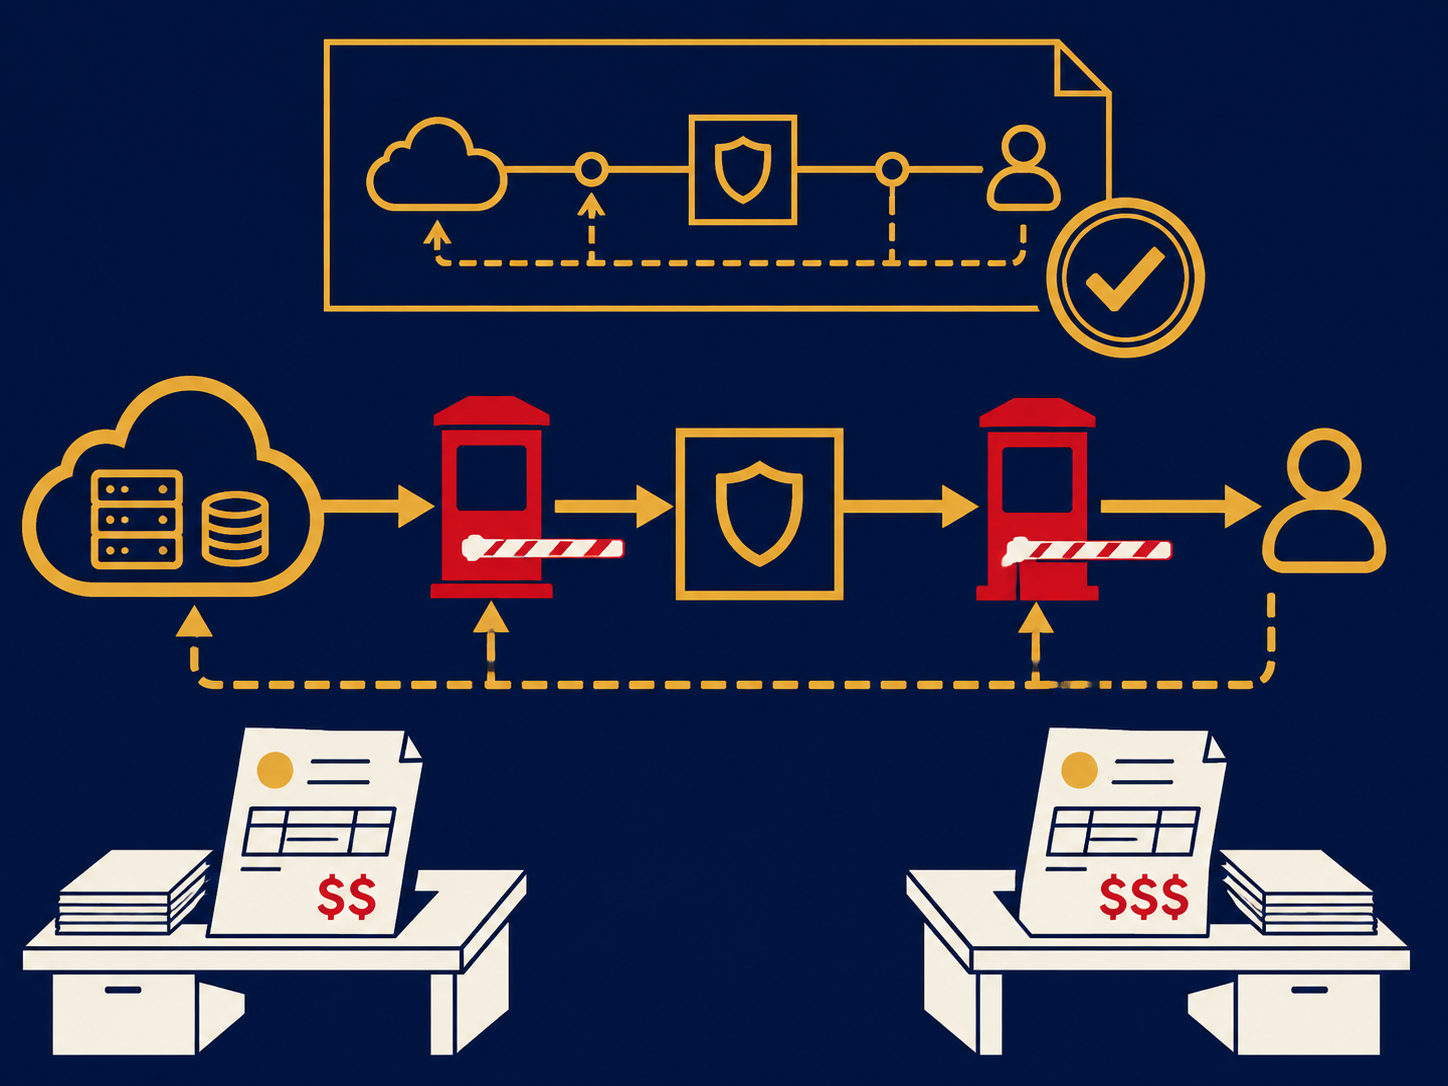
Enforcement points. Endpoint agents watch actions on devices. Email DLP checks outgoing messages, often in a secure email gateway or the email platform itself. Network and web DLP inspect traffic, usually in a security service edge (SSE) service, which requires TLS inspection to see inside encrypted traffic. Cloud DLP, often through a CASB, scans and controls data inside SaaS and cloud storage.
Incident handling. Alerts go to a console where analysts review them, tune policies and, when needed, start an investigation.
When it matters for buyers
- When regulated or contractual data spreads across cloud apps. Health, payment, financial and personal data are the usual starting points.
- When customers, auditors or insurers ask how you prevent leaks. DLP is a common part of the answer.
- When employees leave for competitors. Departing staff downloading files is a frequent trigger for an endpoint DLP project.
- When adopting generative AI. Controlling what goes into public AI tools has become a new DLP use case, alongside managing shadow AI.
- When consolidating security tools. DLP is often already included in SSE, email or productivity licenses; check before buying a standalone product.
Our security service edge overview covers how DLP is delivered alongside web and cloud app controls.
Questions to ask vendors
- Which channels do you cover: endpoint, email, web, SaaS, cloud storage, printing, removable media, AI tools?
- Which operating systems, browsers and unmanaged devices are supported?
- How do you detect sensitive data, and can you match against our own records or documents?
- How do you reduce false positives, and can we run in monitor-only mode first?
- Do you reuse classification labels from our productivity platform?
- How are incidents reviewed, and what does an analyst see, including privacy controls on what’s captured?
- Is DLP included in licenses we already own, and what does adding channels cost?
How it differs from DSPM
Data security posture management (DSPM) finds sensitive data across cloud and SaaS environments, shows who can access it and flags risky exposure, such as an over-shared folder or a public bucket. It is about where data sits and how well it is protected. DLP is about data moving: it watches actions such as sending, uploading and copying and can stop them. The two complement each other, and some vendors now sell them together. Both depend on knowing which data is sensitive, which is why classification and data governance come first.
Problems this helps with
- Employees emailing or uploading customer data to personal accounts
- Worried sensitive files are leaving through USB drives, cloud apps or AI tools
- Auditors or customers asking how we stop data from leaking
- Don't know where our sensitive data lives or who is sharing it