Extended detection and response (XDR) is security software that brings together activity data from several kinds of tools, typically endpoints, identity systems, email, network and cloud services, and analyzes it as one picture to detect attacks and coordinate a response. It extends the approach of endpoint detection and response (EDR) beyond the device, because most attacks touch more than one place: a phishing email, a stolen login, then a compromised laptop.
At a glance
- XDR correlates signals across security layers so related alerts become one incident instead of several unconnected ones.
- Which data sources are covered is defined by each vendor; endpoint is almost always the core.
- “Native” XDR works mainly with one vendor’s tools; “open” XDR ingests data from many vendors.
- Response actions can span layers, such as isolating a device and disabling the related account, where integrations allow.
- It is a technology, not a service: people still need to run it, in-house or through MDR.
What problem it solves
Security teams in mid-sized companies often run separate tools for endpoint, email, identity and firewall, each with its own console and alerts. An attack that starts with a phishing email, moves to a stolen password and ends on a server shows up as three unrelated low-priority alerts in three places. A small team can’t connect them fast enough, if at all.
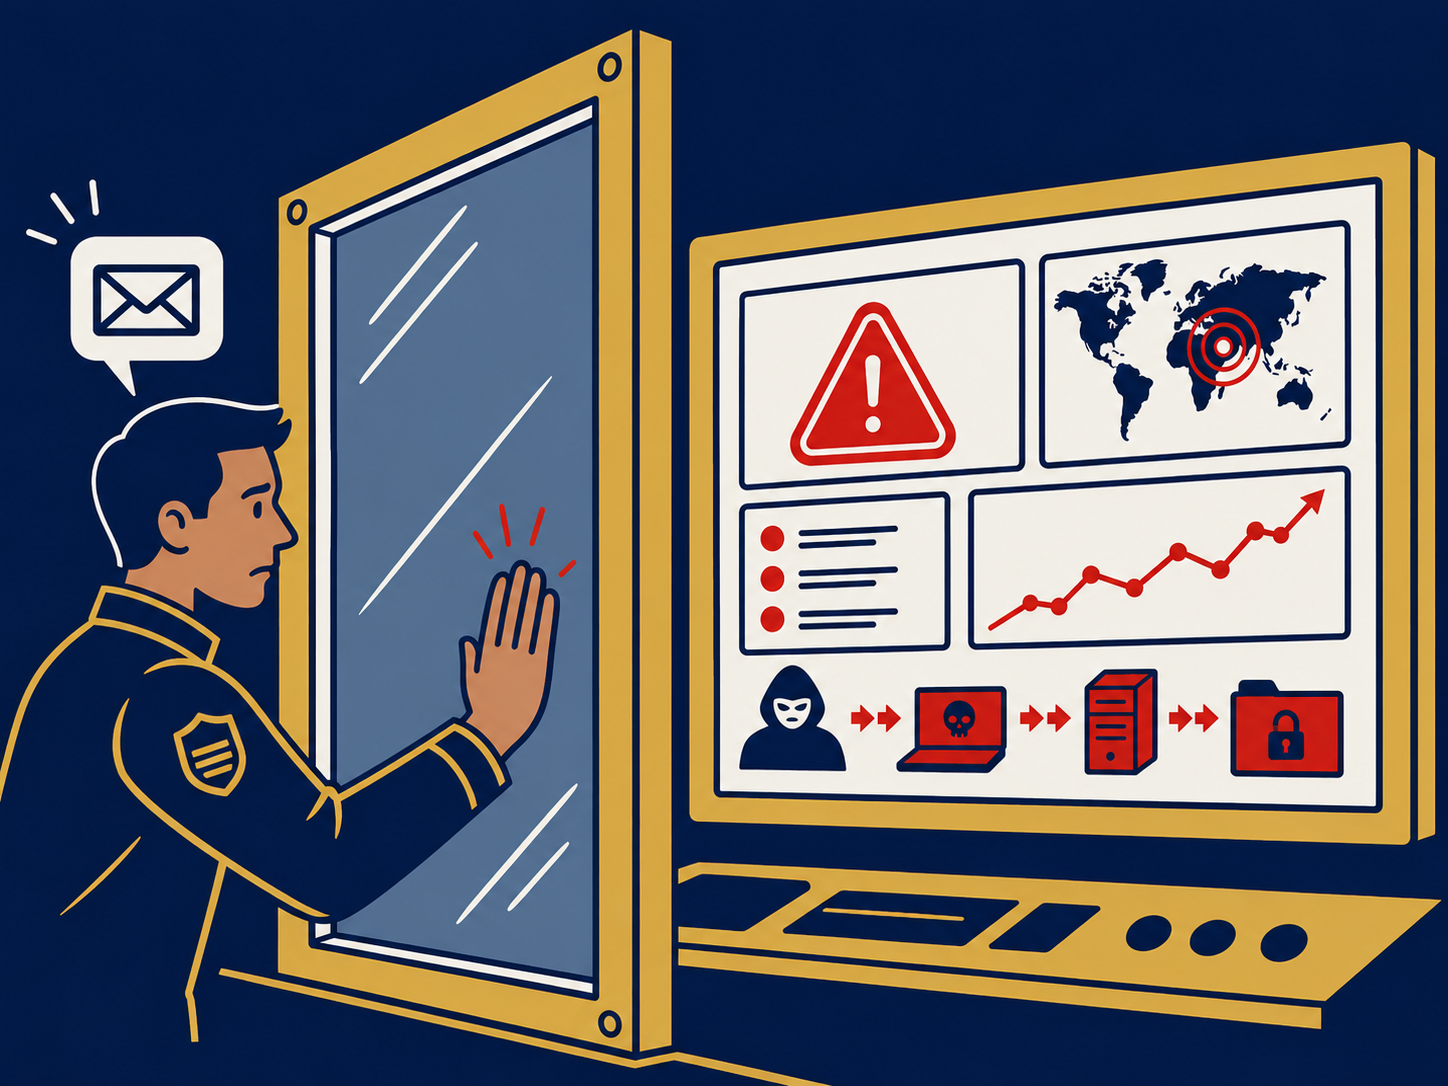
XDR does that correlation automatically. It links events by user, device and time, scores the combined incident, and presents a single storyline with the evidence attached. That reduces the number of alerts analysts have to triage and makes it easier to see the full scope of an attack. For teams that can’t operate a full security information and event management (SIEM) platform, XDR often delivers most of the detection value with less engineering effort.
How it works
Data collection. XDR pulls telemetry from its own agents and from integrations: EDR on endpoints, identity provider sign-in logs, email security, firewalls and network sensors, and cloud and SaaS audit logs. The depth of each integration varies; some provide rich detail and response actions, others only basic alerts.
Normalization and correlation. Data is put into a common format and linked by shared entities such as user, device, IP address and file. Detection rules and analytics look for patterns across sources, like an unusual sign-in followed by a new mailbox forwarding rule and then a suspicious process on that user’s laptop.
Investigation. Analysts see one incident with a timeline across sources, rather than separate alerts, and can search across all collected data.
Response. From one console, analysts can take actions in connected tools, such as isolating a device, forcing a password reset, revoking sessions, quarantining an email or blocking an address. Which actions are available depends on the integrations, and some can be automated with playbooks.
When it matters for buyers
- When you have too many consoles. Consolidating detection into one platform can cut alert volume and tool spend, especially if you already use one vendor for several layers.
- When a SIEM is too much. XDR can be a lighter alternative to building and tuning a SIEM, though it may not meet log retention or compliance reporting needs.
- When choosing an MDR provider. Many MDR services run on an XDR platform, so its coverage defines what the provider can see.
- When attacks are identity- or email-led. Endpoint-only visibility misses the first steps of many business email compromise and account takeover attacks.
Questions to ask vendors
- Which data sources are included natively, which need third-party integrations, and which cost extra?
- For each integration, can you take response actions or only receive alerts?
- How long is data retained, and can we search historical data during an investigation?
- How do you price: per endpoint, per user, by data volume or by module?
- Can XDR meet our log retention and compliance reporting needs, or will we still need a SIEM?
- Do you offer, or support, managed detection and response on the platform?
- If we use your platform with other vendors’ tools, what detections do we lose compared with an all-native setup?
How it differs from EDR, SIEM and MDR
Endpoint detection and response (EDR) covers laptops and servers only; XDR adds other sources and correlates them. A security information and event management (SIEM) platform collects logs from almost anything, keeps them long-term and supports custom searches and compliance reporting, but usually needs more tuning and staff. XDR is narrower and more focused on ready-made detection and response. Managed detection and response (MDR) is a service in which a provider’s analysts operate tools like XDR for you. See our extended detection and response overview and our comparison of MDR vs XDR.
Problems this helps with
- Alerts from endpoint, email and identity tools that nobody connects
- Attacks that start in email or a stolen login, not on a laptop
- Too many security consoles for a small team
- Paying for a SIEM we can't run