Carrier-grade network address translation (CGNAT) is a large-scale form of network address translation (NAT) that an internet provider runs inside its own network, so that many customers share a smaller pool of public IPv4 addresses. Providers use it because public IPv4 addresses are scarce and expensive. For business buyers it matters because a connection behind CGNAT has no public address of its own, which quietly breaks anything that needs to be reached from the internet.
At a glance
- CGNAT is translation done by the provider, in addition to any NAT your own router or firewall performs.
- It is common on cellular, fixed wireless, satellite and many residential-grade broadband services, and less common on dedicated business circuits.
- Outbound browsing, SaaS and cloud apps usually work normally; inbound connections, port forwarding and IP allowlisting often don’t.
- The usual fix is a public static IP address from the provider, a different service type, or IPv6.
- It extends the life of IPv4 but does not replace the move to IPv6.
What problem it solves
The world ran out of unallocated IPv4 addresses years ago, and buying or leasing them on the secondary market costs money. Every new subscriber still needs to reach the internet. CGNAT lets a provider connect many customers through a much smaller pool of public addresses, so it can keep adding subscribers without buying more IPv4 space. For the provider it is an address-conservation tool; for the customer it is a trade-off they often don’t know they have accepted.
How it works
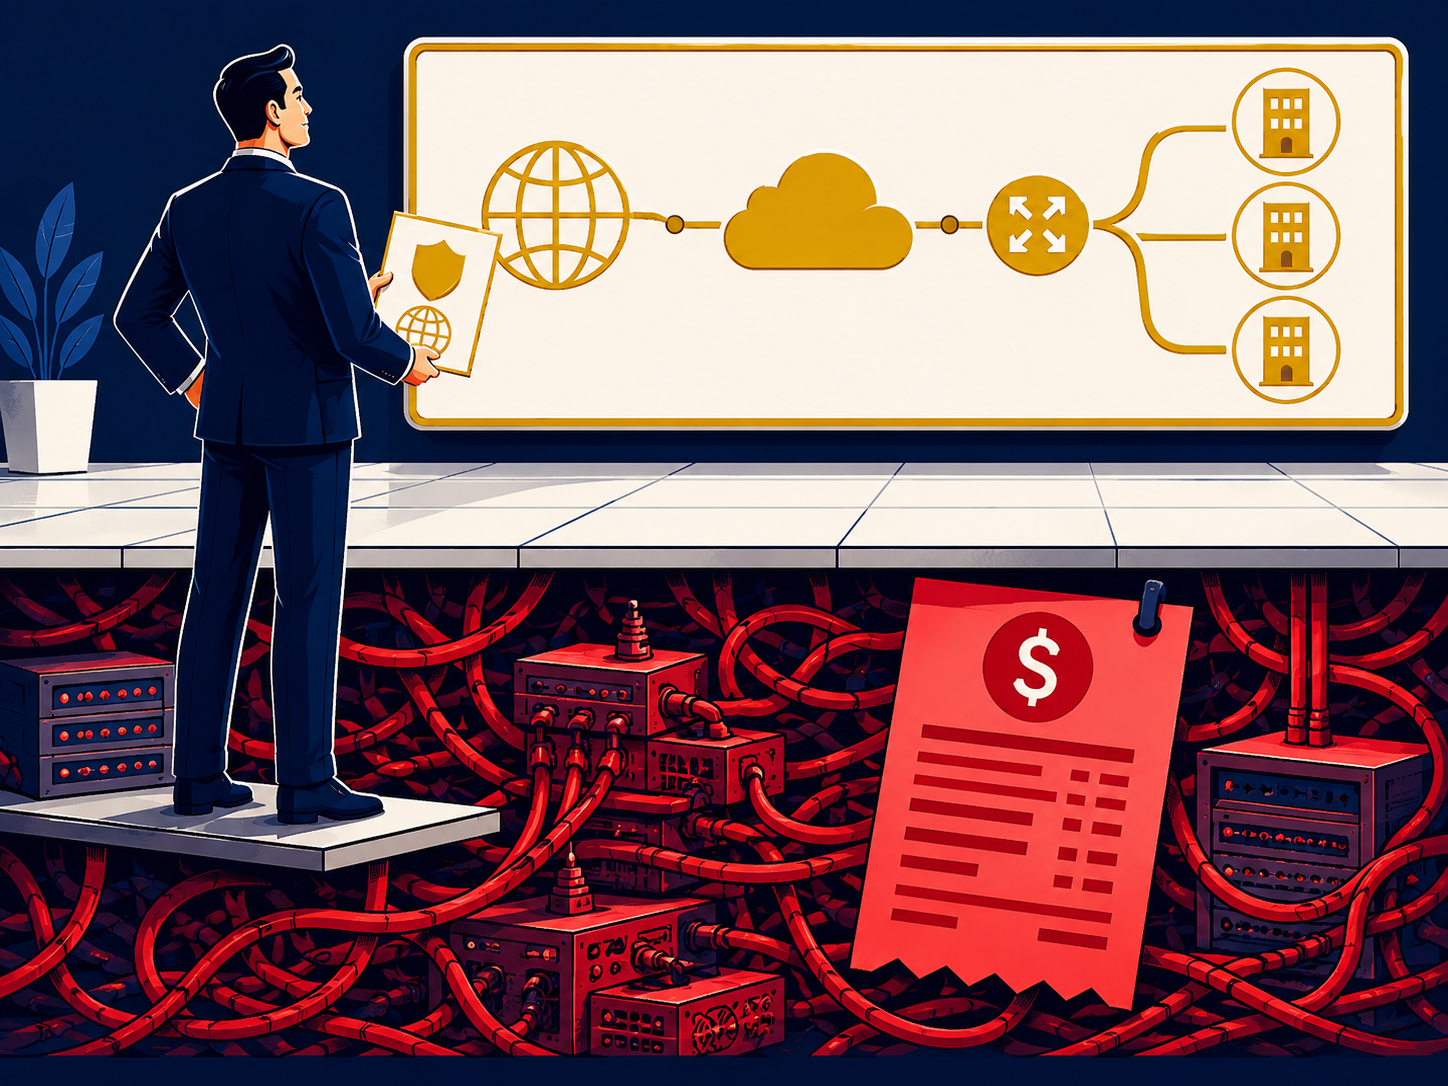
Address sharing. Instead of giving your router a public address, the provider gives it a private one. Providers commonly use the 100.64.0.0/10 range reserved for this purpose, so it doesn’t clash with the private addresses on your own network. Your router translates your devices to that address, and the provider’s CGNAT system translates again to a shared public address. This double translation is sometimes called NAT444.
Port-based tracking. Because many customers share each public address, the CGNAT system tells their traffic apart using port numbers. It keeps a table of every active connection and its mapping.
Outbound only, by default. A mapping is created when a device inside starts a connection. Traffic that arrives unprompted from the internet has no mapping, so it is dropped. That is why inbound services fail.
Logging. Because one public address represents many customers at once, identifying who used it at a given moment requires the provider’s translation records. Many providers keep these logs for abuse handling and legal requests; what they must keep, and for how long, depends on the jurisdiction.
IPv6 alongside. Many providers run IPv6 in parallel (dual stack). IPv6 traffic usually doesn’t need CGNAT at all, because there are enough IPv6 addresses for every device.
When it matters for buyers
- Remote access to a site. Cameras, door controllers, building systems, servers or a VPN endpoint that must be reached from outside won’t be reachable behind CGNAT without a public address or a cloud relay service.
- IP allowlisting. If a bank, payment processor or SaaS app only accepts connections from your office’s IP, a shared and possibly changing address won’t work reliably.
- Backup links. Cellular failover and fixed wireless or satellite backups are often behind CGNAT, so inbound services that work on the primary link can stop during an outage.
- Shared reputation. If another customer on the same public address misbehaves, sites may show you CAPTCHAs or block you.
- Choosing a service type. Business plans with a static IP address or dedicated internet access avoid most of these issues.
Questions to ask vendors
- Does this service use CGNAT, and is that the same on every plan and at every location?
- Can I get a public static IPv4 address, and what does it cost?
- Is IPv6 supported natively, and will my equipment receive a routed IPv6 prefix?
- Will inbound connections, port forwarding and site-to-site VPNs work on this service?
- On backup or cellular links, will the public address match the primary link, and if not, how do I handle allowlists?
- How long do you keep translation logs, and how do you handle abuse reports that involve a shared address?
If you need a reachable address at a site, compare internet access options with static IPs included.
How it differs from NAT
Ordinary NAT runs on your own router or firewall: it lets the devices in one office share the single public address your provider gave you, and you control its settings, including port forwarding. CGNAT runs in the provider’s network and shares one public address among many customers. You can’t configure it, port forwarding through it isn’t available, and the public address you appear from is not yours alone. Behind CGNAT you usually have both: your own NAT and the provider’s.
Problems this helps with
- Can't reach cameras, servers or a VPN at a site from outside
- Port forwarding on our router doesn't work
- Our site's public IP keeps changing or is shared with other customers
- A partner can't allowlist our office's IP address